
Supply chain security: Risks, controls and network defense
Learn what supply chain security means, the common risks and controls, and how network-level threat defense protects shared WiFi and connected environments.
Published November 17, 2026
You are looking at a vendor spreadsheet that says every supplier is "approved," and a ticket that says a payment terminal cannot reach its vendor this morning. Procurement wants a yes or no on the renewal. Operations wants the registers back online. Neither document tells you whether the vendor's cloud host, update server, or identity provider is what just failed.
That is the everyday shape of supply chain security. The risk is not only the company named on the contract. It is the shared platform behind several contracts, the update that arrives already trusted, and the partner login that still works because nobody reviewed it this quarter.
I would start by naming the handful of dependencies you cannot run without, then ask what evidence you hold for each one. A logo on a questionnaire is not a decision.
Table of Contents
- What Supply Chain Security Means and Why It Matters
- Where Supply Chain Risk Enters and Why Partners Are Weak Points
- How Software Supply Chain Attacks Spread
- Controls That Shrink Supply Chain Risk
- Managing Nth-Party Risk You Cannot See
- Where Network-Level Threat Defense Fits
- Decide Which Supply Chain Gap to Close First
What supply chain security means and Why it matters
Supply chain security means protecting every supplier, service, software component and route that delivers what your organization depends on, and deciding how much trust each link deserves.
A building with a strong front door and an unsecured loading bay has a supply chain problem, not a door problem. The same pattern shows up in operations. Your own firewall can be tight while a carrier, a software vendor, or a cloud region still decides whether orders, care records, or guest WiFi stay up.
The scale of that exposure is structural. The OECD supply chain resilience review reports that intermediate products accounted for up to 60% of global trade in 2020, so goods and services often cross borders several times before they reach a user. Each crossing is another supplier, port, platform, or contract that can fail.
Concentration beats a long vendor list
Approximately 30% of exported products are subject to high concentration among a small number of trading partners, and cases of suboptimal diversification were 50% higher in the 2020s than in the late 1990s, according to that same OECD review. A register of 400 vendors can still hide one identity provider, one cloud region, or one port that several of them share.
Bringing production home is not an automatic fix. OECD modeling of a broad relocalization scenario shows global trade could fall by more than 18% and global real GDP by more than 5%, without consistent resilience gains. What holds up better is visibility of critical dependencies, diversification, substitution options, and coordinated risk management. Withdrawal from trade does not replace those four.
Where supply chain risk Enters and Why partners are weak points
| Entry point | How it fails | Warning sign |
|---|---|---|
| Direct suppliers | A vendor breach exposes shared data or access | Vendor refuses to share audit or security evidence |
| Logistics and ports | Delay or tampering halts inventory or shipments | One carrier or port with no tested fallback route |
| Software vendors | A compromised update reaches your systems | No SBOM or no signed build provenance |
| Cloud and managed services | A provider outage cascades into your operations | One provider hosts several critical services |
| Identity and access providers | Stolen partner credentials open internal systems | Shared accounts or no MFA for partner logins |
| DNS and network providers | Malicious domains are reached through an unchecked lookup | Guest or BYOD traffic runs without lookup filtering |
Every row is a path an attacker or an accident can use without touching the systems you run yourself. A cleaner who keeps a master key does not need to defeat the vault. A thief rarely picks the vault when the cleaner's keys open the back door.
Why the weaker partner gets chosen
The World Economic Forum's 2023 Global Cybersecurity Outlook found that 27% of business leaders and 14% of government leaders considered third-party organizations far less cyber-resilient than their own organizations. Attackers follow that gap. They target the vendor, the service desk, or the software dependency instead of the better-defended primary organization.
Evidence from Verizon's 2024 Data Breach Investigations Report, summarized by the World Economic Forum, showed incidents involving software vulnerabilities increased by 180% in 2023 compared with the previous year, and 15% of those incidents involved a third-party supplier. The wider volume is large enough that waiting for a perfect inventory is a poor plan. The Forum reported an estimate of approximately 2,220 cyberattacks per day in 2023, equivalent to more than 800,000 attacks during the year.
What a perimeter cannot see
A firewall at your edge does not inspect a partner's build server, and it does not notice that three "independent" vendors all sit on one cloud account. Controls have to reach partners and digitally connected services whose compromise could stop operations, expose data, or break trust across the network.
Practical rule: List every supplier that holds access, data, or a service you cannot run without, then mark which of the six entry points each one uses.
How software supply chain attacks Spread
Say a library your point-of-sale vendor relies on is maintained by one developer. Phishing takes that account. The repository is changed. The build system packages the tampered code. The artifact is signed with the pipeline's normal key and published. Your vendor ships the update, and your registers install it because the update channel is approved.
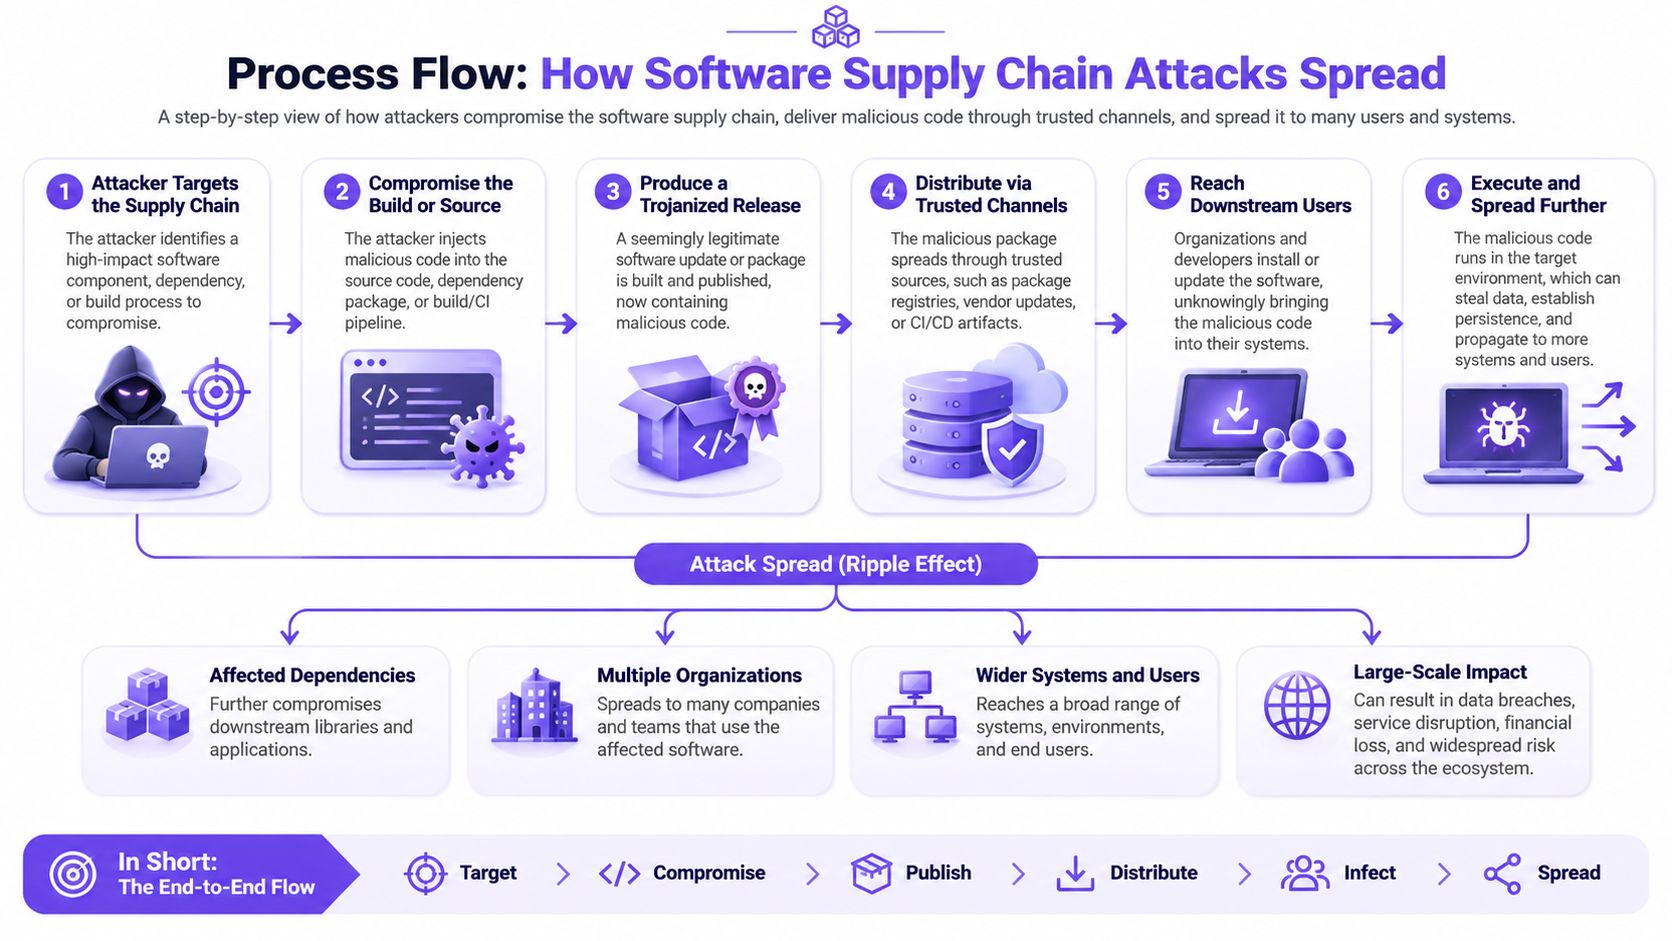
Each handoff inherits trust from the one before it. That inherited trust is the weakness. Nobody at your site clicked a suspicious link. The malicious code arrived as a routine release.
Why the firewall stays quiet
ENISA's threat landscape for supply chain attacks reported that these attacks increased in number and sophistication in 2020, and estimated that 2021 attacks would be approximately four times more numerous than in 2020. About half were attributed to advanced persistent threat actors, whose resources make a perimeter-only defense a poor match. The lookup and the download look like every other patch Tuesday.
The same chain is not limited to application code. It runs through DNS providers, cloud platforms, certificate authorities, managed libraries, CI/CD services, and threat-intelligence feeds. A poisoned feed can mark a bad domain as safe. A weak certificate authority can make a fake update look genuine.
What to attach to each dependency
Treat supplier risk as an attack path, not a questionnaire score.
- Owner: One named person who can pull the dependency or call the vendor.
- Criticality: Whether payroll, orders, clinical systems, or guest access stops if it fails.
- Permitted flows: Which data and which networks that supplier may touch.
- Recovery: How you isolate it and how you prove service is restored.
- Replacement: A tested alternative, or a written decision that none exists.
The control objective is to shorten the time from supplier compromise to detection, containment, and verified restoration. An annual assessment does not do that on its own.
The handoffs in that chain are easier to see when you watch them as a sequence rather than a policy paragraph.
Controls that shrink supply chain risk
| Control | What it covers | Evidence to keep |
|---|---|---|
| Vendor register | Every supplier with access, data or an operational role, with owner, criticality rating, data flows, recovery procedure and replacement option | Dated register reviewed at least yearly |
| Contractual security clauses | Breach notification, audit rights and patch timelines | Signed clauses with stated notice periods |
| SBOM at build time | Components, versions, suppliers, dependencies and licenses | Signed SBOM stored with each release |
| Provenance and artifact signing | Proof that software was built from a known source | Signed provenance record per artifact |
| VEX statements | Vulnerabilities confirmed unreachable or unexploitable in your configuration | Dated VEX statement for each advisory |
| Supplier account access | Limits partner logins to the systems they need, with MFA | Quarterly access review log |
| Incident reporting and recovery drills | Speed of containment and verified restoration | Drill report with time to restore |
A register without an owner is a phone book. A contract without a notice period is a hope. Keep the evidence column, not only the policy name. Segmenting partner access from staff and guest traffic is part of the same habit, and network segmentation is where that boundary is designed.
From inventory to a release decision
CISA describes a software bill of materials as a machine-readable, nested inventory of the components and dependencies in a software product, used to improve transparency and support vulnerability-response decisions. An SBOM only becomes a control when each component is tied to a stable identifier such as a package URL or Common Platform Enumeration, plus version, supplier, dependency relationships, license, and provenance, then compared continuously with vulnerability and exploitability intelligence.
CISA also recommends that you obtain provenance and verify the software was built from an understood source, not downloaded or altered in delivery. The workflow I would insist on is short.
- Generate the SBOM at build time, not after the release is already in production.
- Sign the artifact and the provenance metadata.
- Store both with immutable release records.
- Block promotion when a critical component lacks provenance, contains an exploitable vulnerability, or breaks an approved dependency policy.
A VEX statement records that a listed vulnerability is not reachable or exploitable in your deployed configuration. That stops a team from patching everything on a scanner export while the one reachable flaw waits. An SBOM sitting in a compliance folder does not shrink risk. An SBOM that blocks a release, or that ranks what to fix first, does.
Managing Nth-Party Risk You Cannot See
Fewer than half of organizations monitor cybersecurity across even half of their supply-chain tiers, and 79% report that less than half of their nth-party ecosystem is covered by security programs, as covered by TechDay's reporting on supply chain cyber readiness. Sending another questionnaire to the companies you already contract with will not close that gap.
More forms do not find the subcontractor, the shared cloud tenant, or the library your vendor never named. Concentrated dependencies and single points of failure matter more than the headcount of vendors. Boards and regulators increasingly want evidence that risk is prioritized, not only documented.
Answer these three questions this quarter, even if the answers are incomplete.
- Indirect support: Which suppliers you never contracted still underpin payroll, orders, or clinical systems?
- Shared providers: Which cloud, identity, or managed-service names appear behind several of your vendors?
- Failure: What stops if one cloud, identity, ERP, or managed-service provider fails on a Tuesday morning?
Rank what you cannot fully see
| Factor | Lower concern | Higher concern |
|---|---|---|
| Business criticality | Supports a non-essential internal tool | Supports payroll, orders or patient records |
| Concentration | Used by one of your vendors only | Shared by several of your vendors |
| Substitutability | Alternative tested within a week | No tested alternative exists |
| Geographic exposure | Single country with redundant route | Single region or single port |
| Incident blast radius | Affects one location or one team | Affects multiple locations or several services |
Score each factor from 1 (lower concern) to 3 (higher concern). Add the five scores. Rank by total, and break ties by incident blast radius. Review the top five first and write down which factor drove each score. Pair that ranking with what your threat intelligence feeds cover, so a shared provider is not invisible just because no direct contract names it.
Visibility will never be complete. The ranking decides where effort and evidence go first. A supplier scored 15 because it is shared, unsubstitutable, and tied to orders outranks a long list of low-scoring tools, even if those tools returned prettier questionnaires.
Where network-level threat defense Fits
Think of a checkpoint, not a moat. Every destination is checked before anyone walks through. That check sits beside identity, software provenance, and supplier controls. It does not replace them.
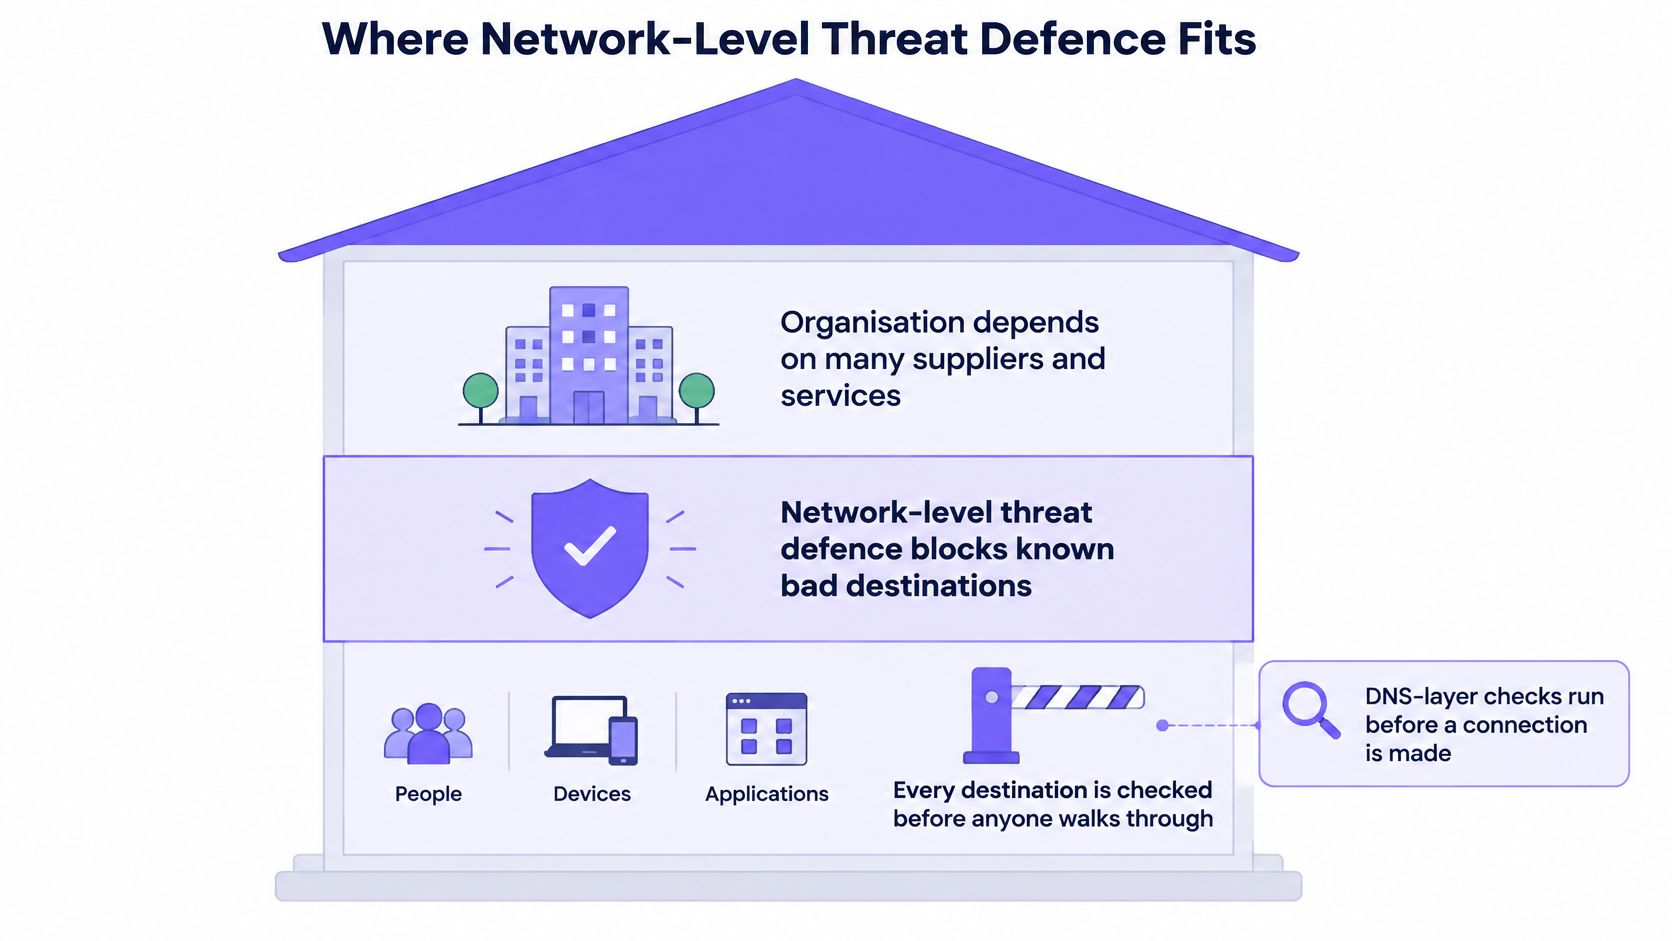
DNS-layer checks run before a connection starts. They can stop command-and-control callbacks from an infected device, plus phishing and malware domains, without an agent on the device. That matters on guest, public, and student WiFi, where registers, scanners, cameras, and visitors' phones never take your endpoint software. A lookup filter still sees the name those devices ask for.
Policy that matches the room
Rules should differ by network segment, venue, and time of day. A hotel lobby at 10:00 PM is not the same risk as a staff VLAN at 10:00 AM. Stricter evening and weekend rules, with a report of what was blocked, give operations and procurement a shared record instead of a vague "the WiFi is filtered" claim. DNS security is the layer that makes that check, and it belongs in the stack as one band, with identity, software, and supplier controls still visible around it.
What this layer cannot do
- It does not repair vulnerabilities in your own code or in a vendor's update.
- It does not stop connections made straight to an IP address with no prior lookup.
- It cannot see inside encrypted content when the control is DNS only.
- It does not replace contracts, inventories, provenance, or a ranked supplier list.
I would not sell this layer as complete protection. I would place it where unmanaged devices and shared networks are the failure path, and keep SBOM, access review, and nth-party ranking for the paths a lookup will never see.
Decide which supply chain gap to close first
- List the top five suppliers from your nth-party ranking, with the five factor scores beside each name.
- Check each one against the control table. Mark the missing evidence: register entry, signed clauses, SBOM, provenance, VEX statement, account review, or drill record.
- Set a hard threshold. Any supplier with access to customer data or a critical service, and no evidence of controls, goes first.
- Close the largest gap first. That might be an SBOM request for a software vendor, or a register entry for the cloud or identity provider several vendors share.
- Where guest, public, or student devices share infrastructure, add a network-level threat defense layer. If the property runs change control, pilot on one network before anything wider changes.
When you ask a vendor for assurance, request certifications such as ISO 27001 or Cyber Essentials with proof of scope, not a logo on a slide. Purple Shield is certified and aligned to recognized security and child-safety standards, including ISO 27001, CCPA/CPRA, and Cyber Essentials. On Open networks Shield applies a strict, family-safe policy, on Secure networks threat defense comes first, and on xPSK networks safeguarding is set per group. For estates that run change control, Purple plans a pilot of Shield on one SSID with your team or your IT provider before anything wider changes.
Pick one missing piece of evidence this month. Name an owner and a review date before the meeting ends.
Purple Shield checks domain lookups on guest, public, and shared WiFi before a connection starts, blocking phishing, malware, and command-and-control destinations on devices that never take an agent. That layer sits beside supplier ranking, SBOMs, and access reviews. It does not replace them. If shared networks are the gap you ranked first, see how Purple Shield applies threat defense per network, per venue, and per schedule.